The morning after a deploy
Today's footprint against yesterday's: a new open route or a forgotten workers.dev address is on your list before a stranger finds it.
Paxen probes your internet footprint every day like an AI agent swarm and hands you a plain-English, fix-first list.
About a minute. Public certificate and DNS records only. No account.
northwind-demo.comDaily run finished 5:52am · 214 addresses checked · Set aside as noise: 188 · Yours to act on: 3
One action: require the key your other routes use, then replace the webhook address.
One action: rotate it into your vault; Paxen updates the app that uses it.
One action: turn the workers.dev address off.
The problem
One person with an AI agent swarm can probe your whole internet footprint in under a day. Paxen gives solo builders and companies of 5 to 200 people the attacker's view every morning, written for a team with no security staff.
find an open route that answers without a sign-in, a leftover admin page, or a second workers.dev address beside your domain.
claim a dangling DNS record, send mail as you, or use a live token from a public page.
feed instructions to an AI agent with broad permissions through an email, a web page or a chat.
How it works
Paxen reads certificate transparency records and DNS and maps what answers from the internet: free, about a minute, no account.
Add one DNS TXT record at _paxen.yourdomain.com to turn on the full active check set and a daily rerun with a diff of anything newly exposed.
Link Cloudflare, GitHub, Google and 1Password read-only, with every scope shown, then work down your ranked list one action at a time.
The product
Everything an attacker would try, checked every day and ranked into one plain-English list.
Paxen maps every domain, subdomain, Cloudflare Worker, Pages site, tunnel and webhook you own, and takes an exposed address off the internet in one click, with an undo.
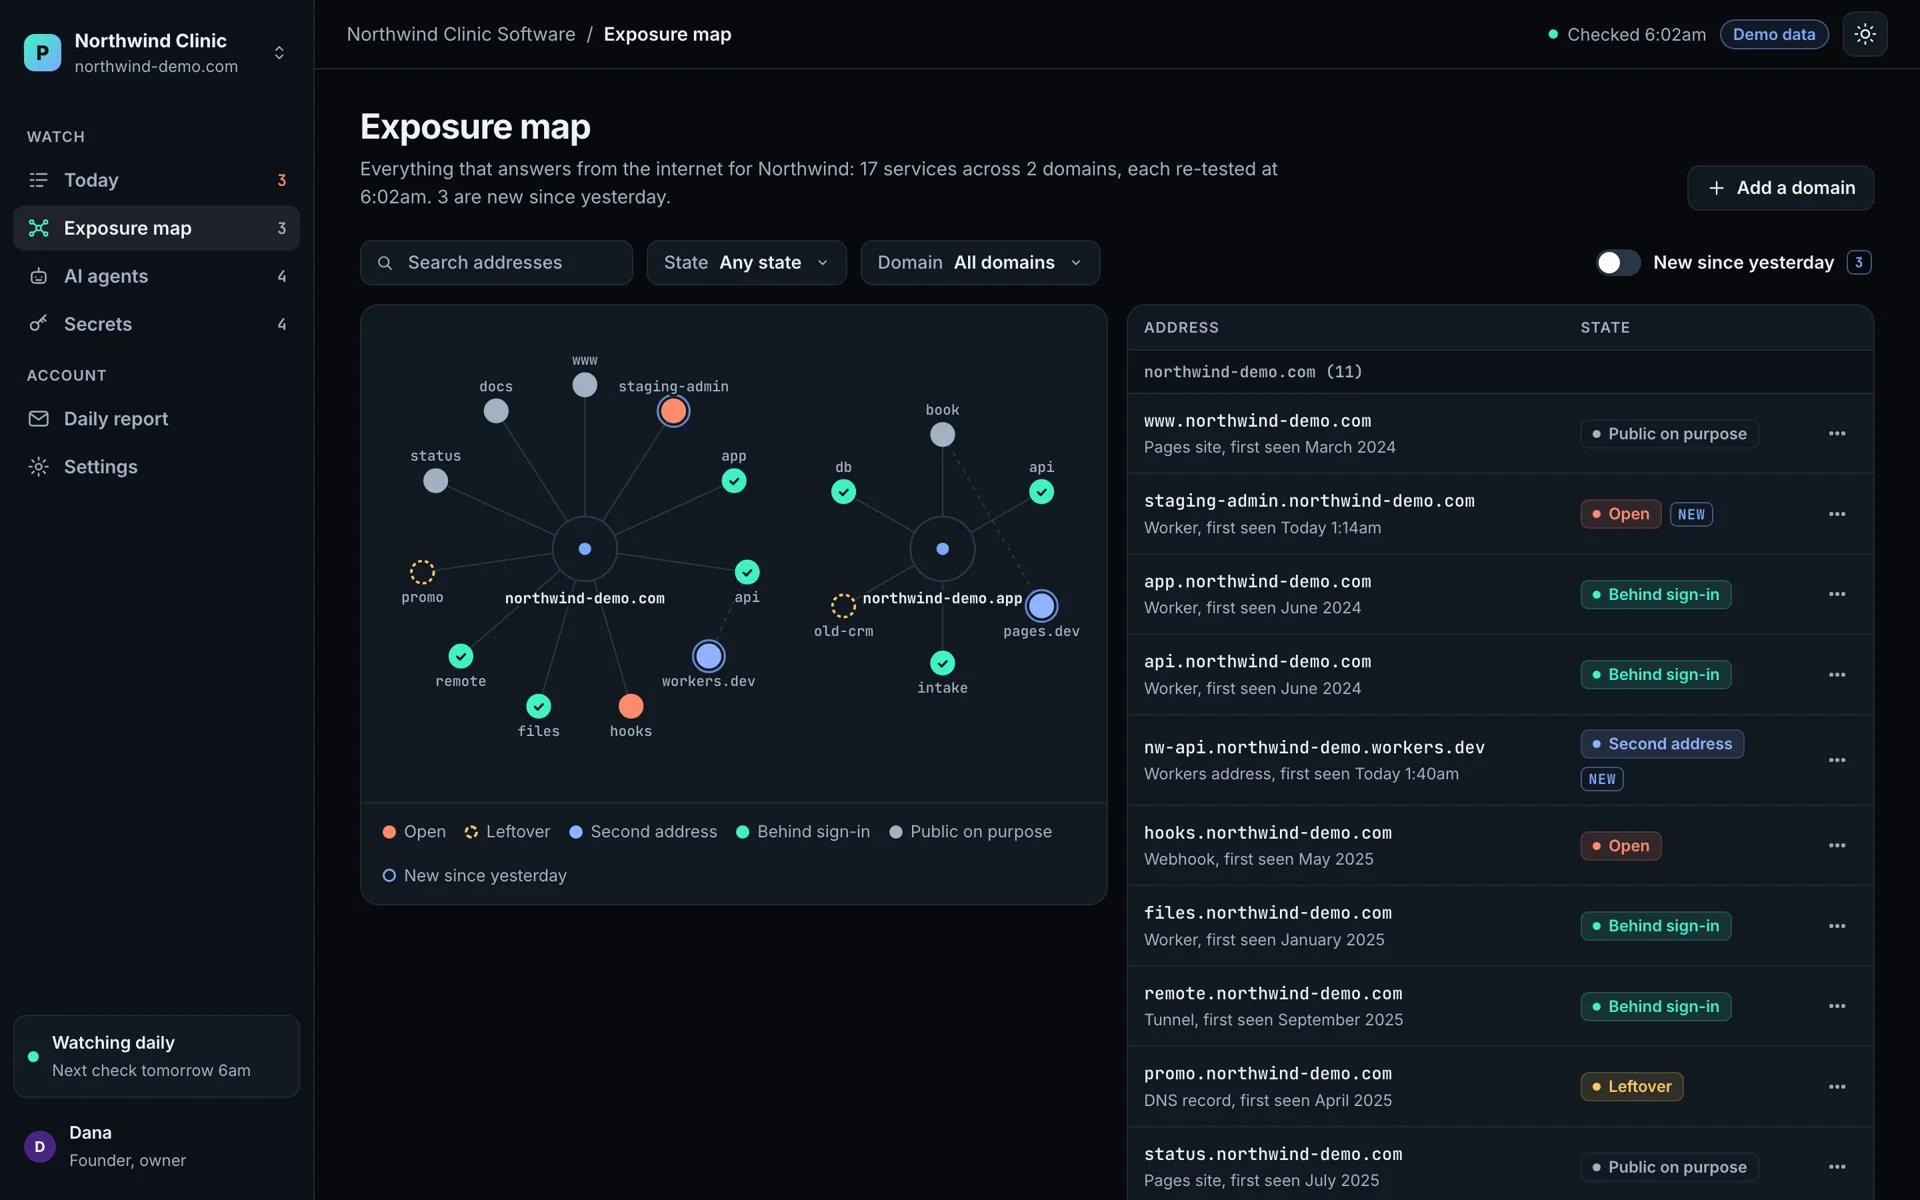
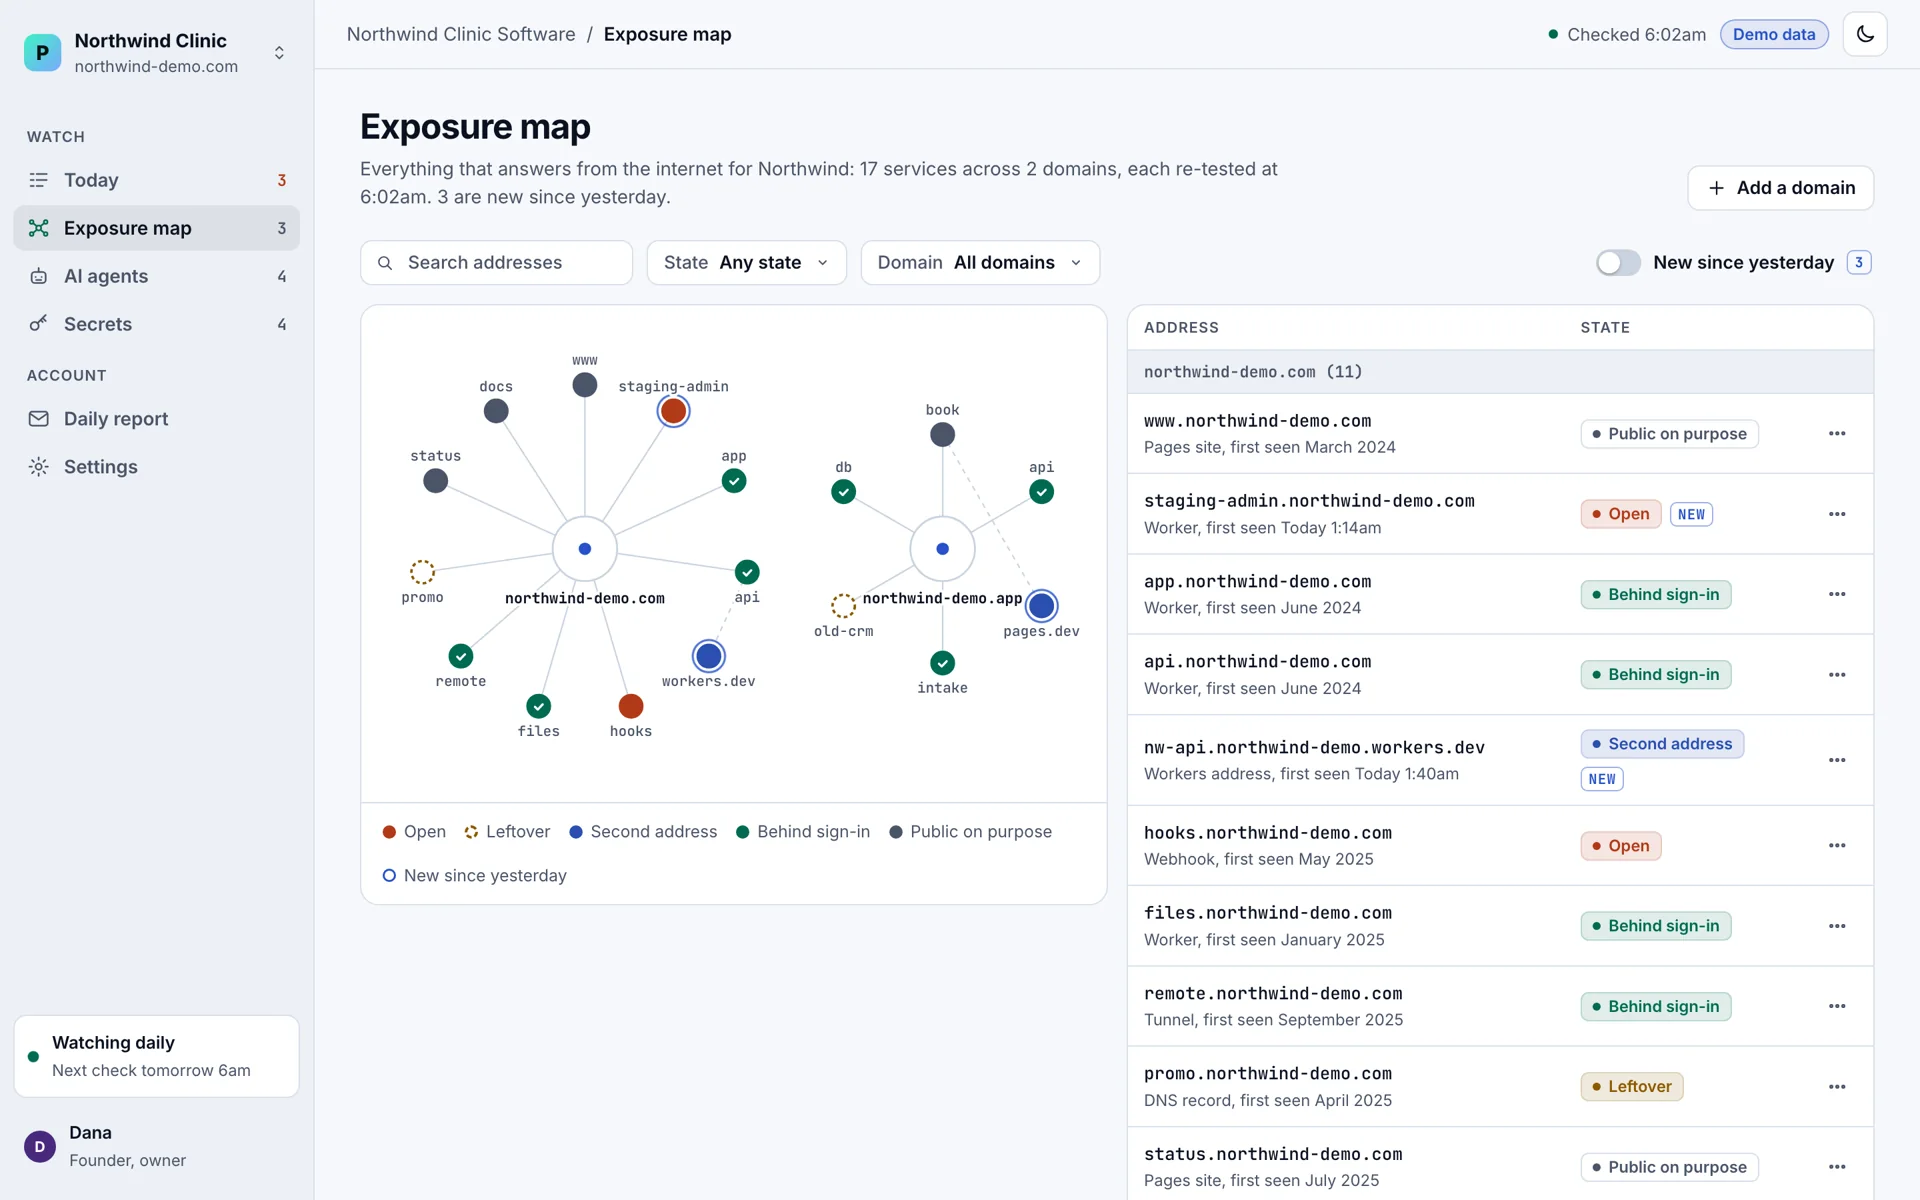
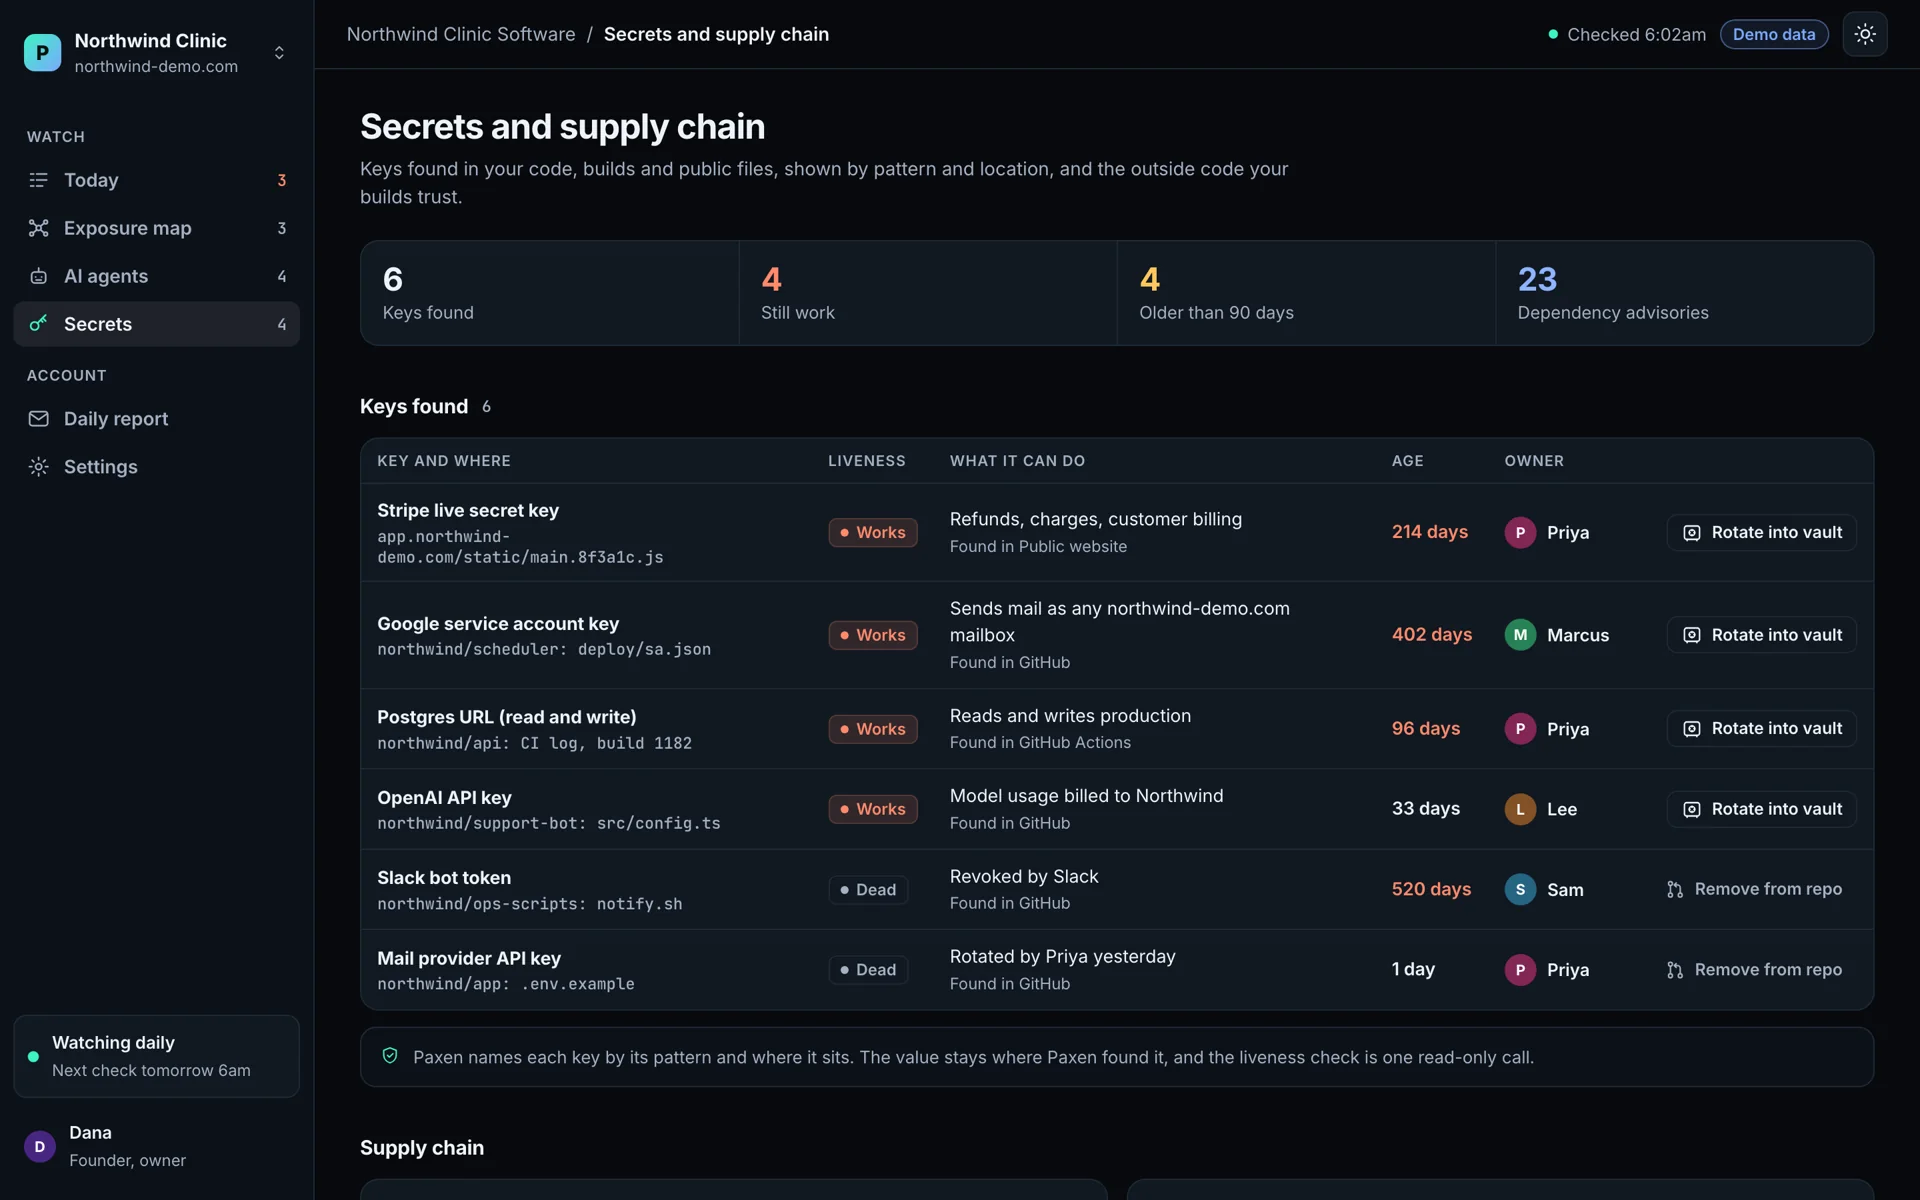
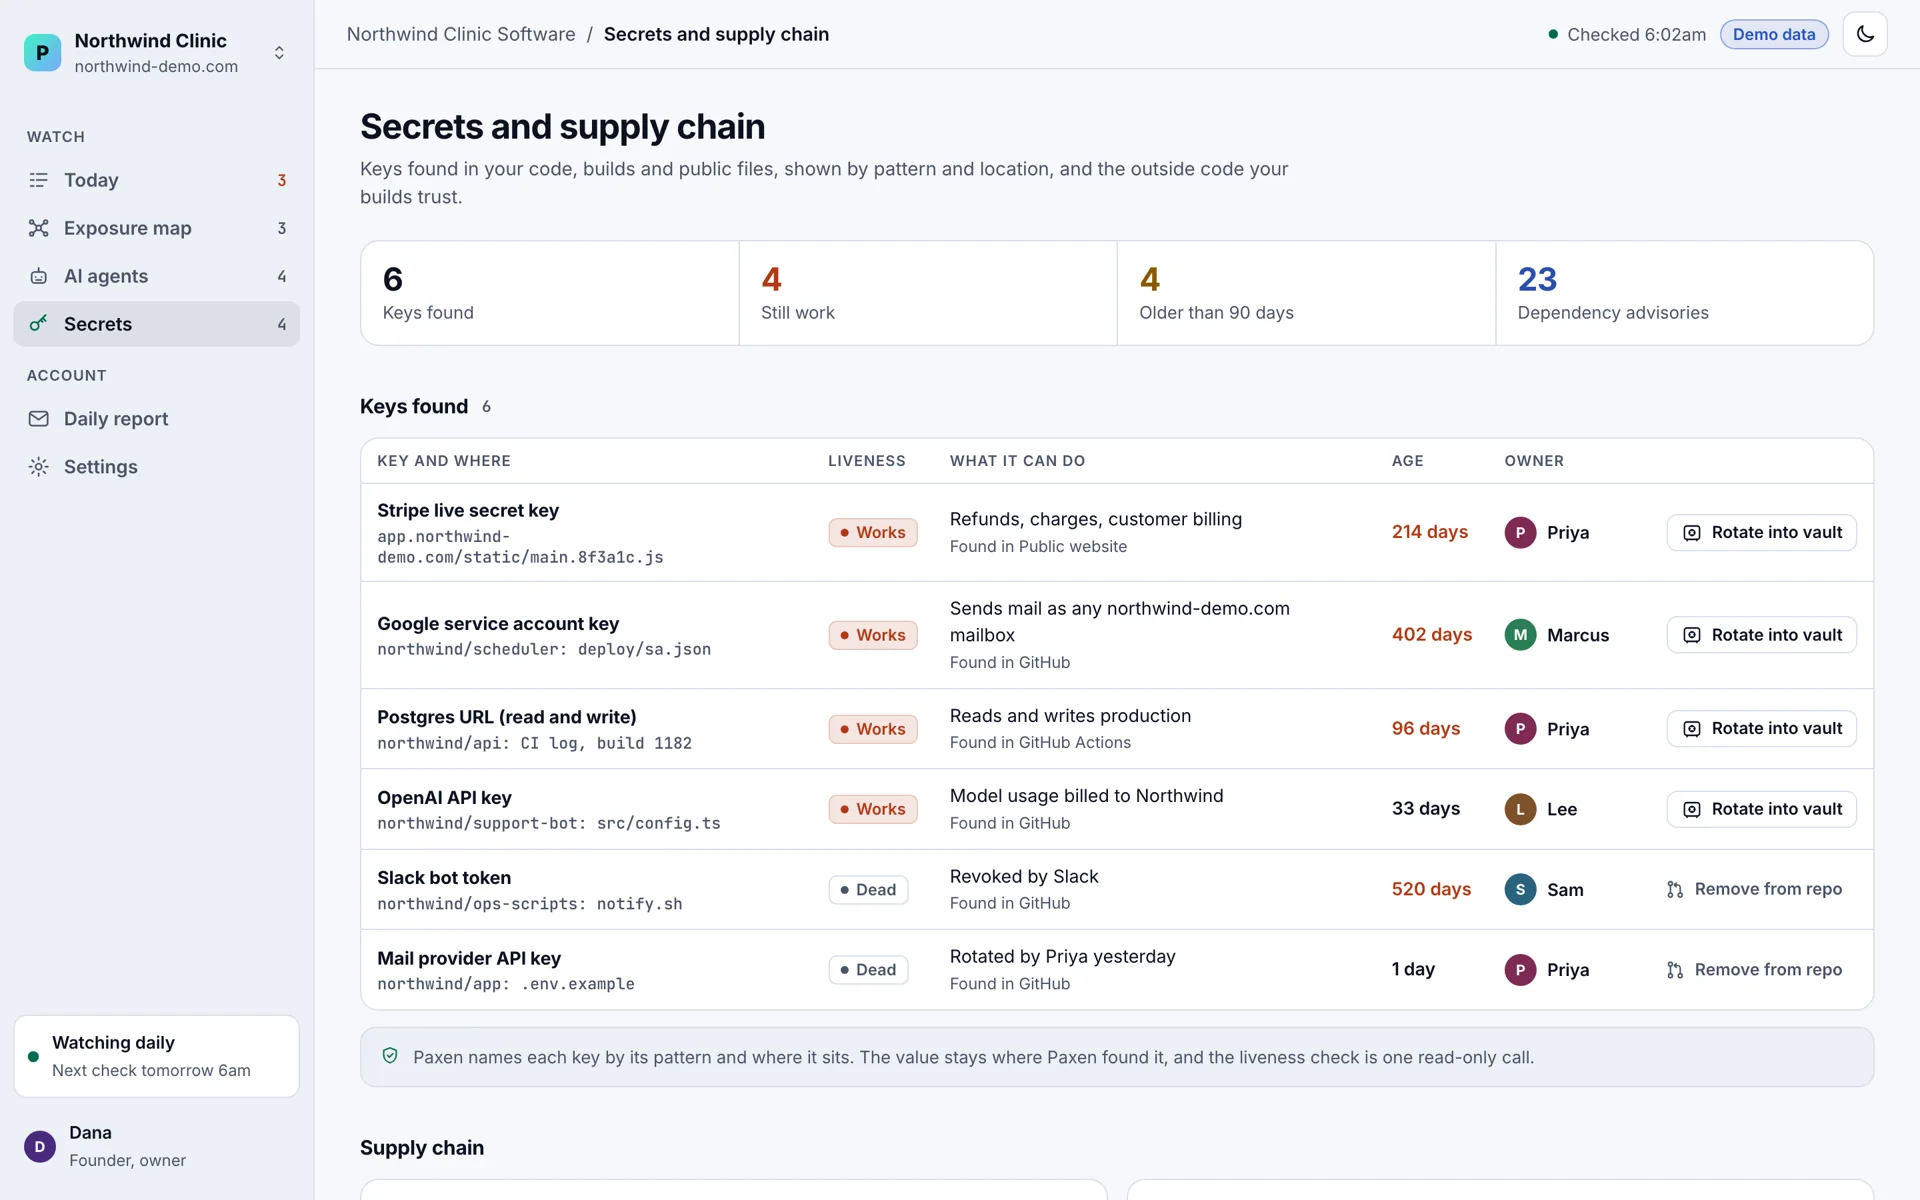
Paxen finds keys and tokens in repos, .env files, CI and public pages, and reports every match by its pattern name, never its value.
Paxen locks down third-party code by opening the pull request for you, and watches live supply-chain campaigns against your repositories.
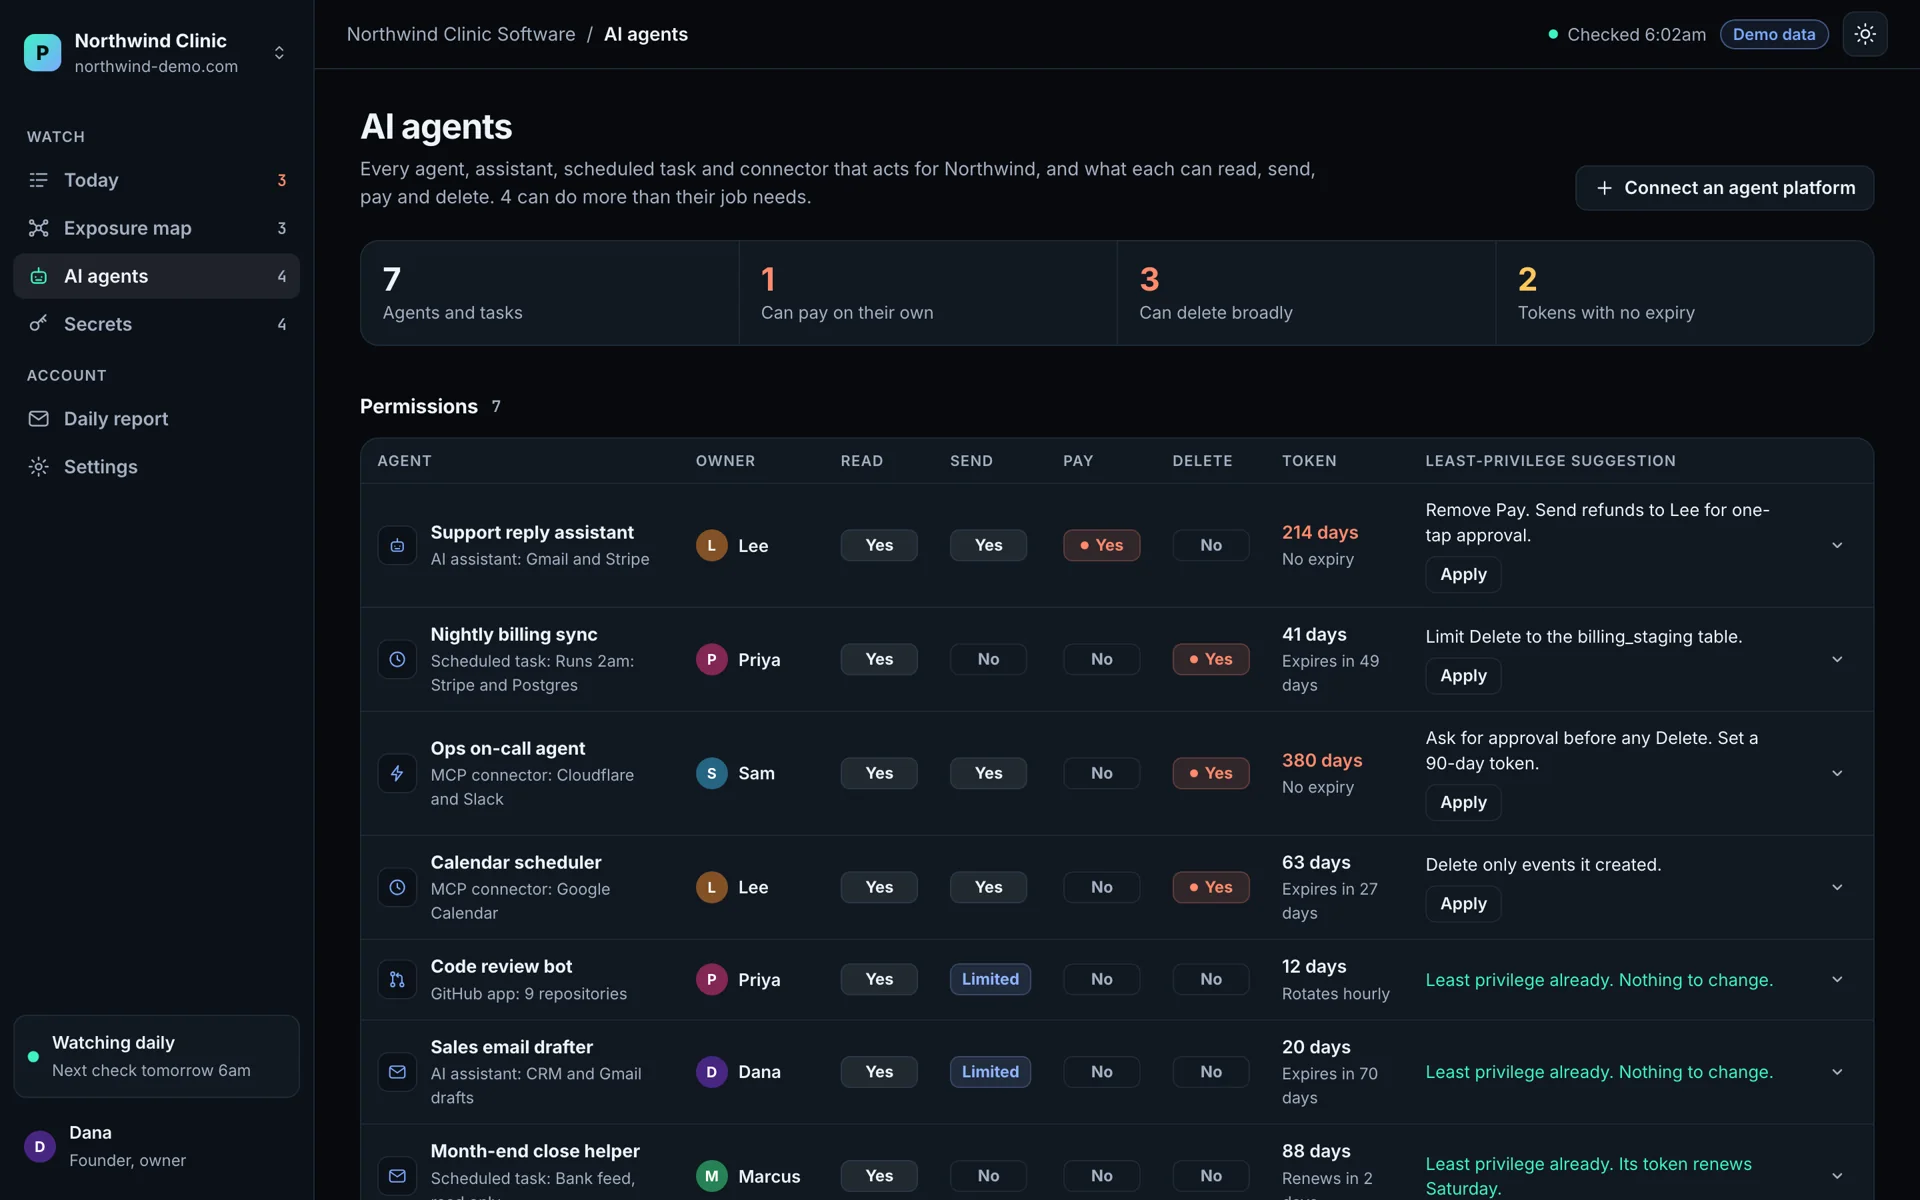
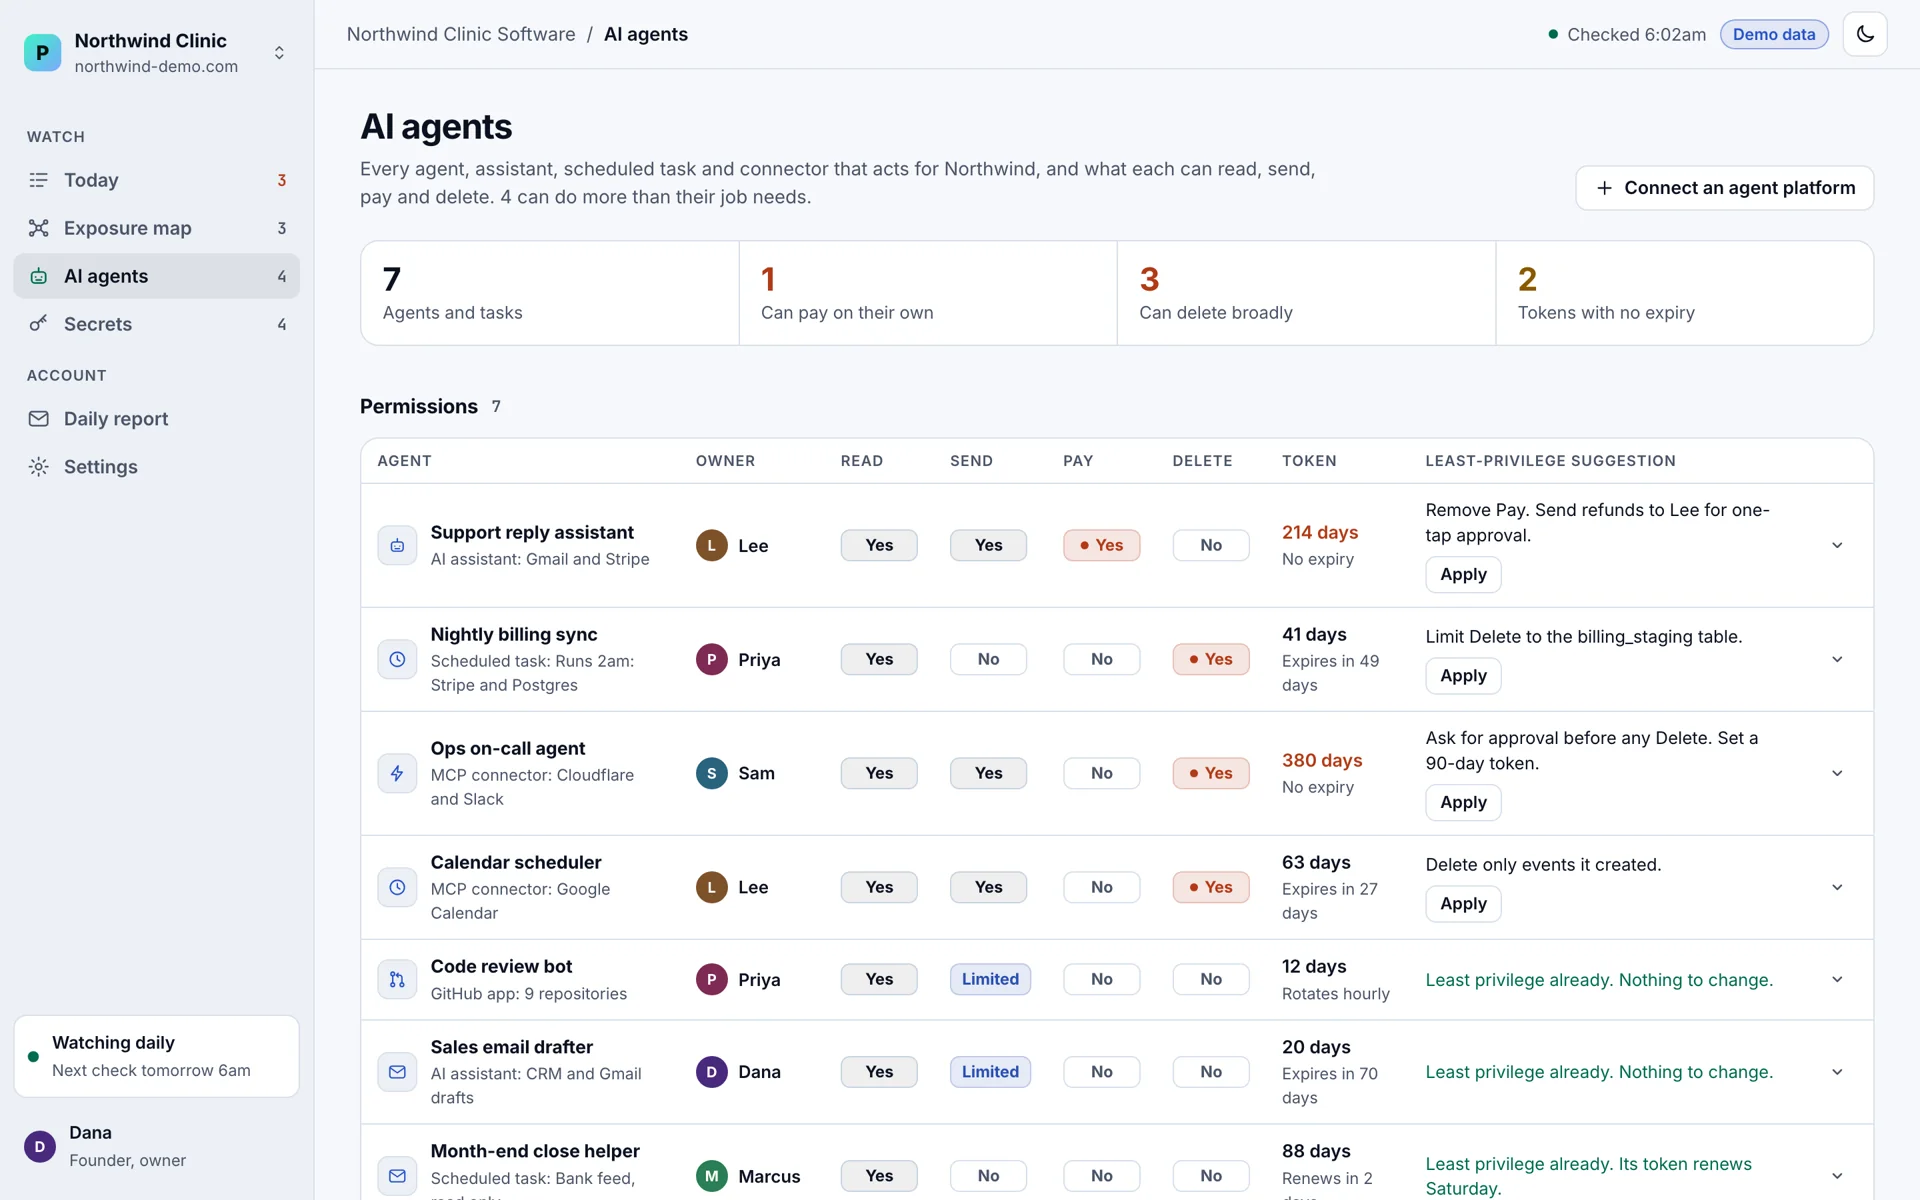
Paxen inventories every AI agent, assistant, scheduled task and MCP connector, with what each can read, send, pay and delete.
Open-source analyzers and a frontier model read the risky paths every week: sign-in, webhooks and file parsers.
# risky paths read this week
src/auth/session.ts        model   token never expires
src/webhooks/stripe.ts     semgrep signature checked after parse
src/upload/csv.ts          codeql  clean
package-lock.json          osv     2 advisories, 1 reachable

# fix pull requests
#418  expire sessions after 12 hours   written: GPT  reviewed: Gemini  ready
#419  verify signature before parse    written: Gemini  reviewed: GPT  ready
Paxen folds every module into one ranked list, a morning email, and records your customers and insurers can check.
The fix-first list
Rules set the severity. A model on our own hardware sorts the routine findings, then GPT and Gemini rank and cross-check the list, so every line you read has one plain-English action and one named owner.
Open a line to see what Paxen saw. Sample data.
The morning report
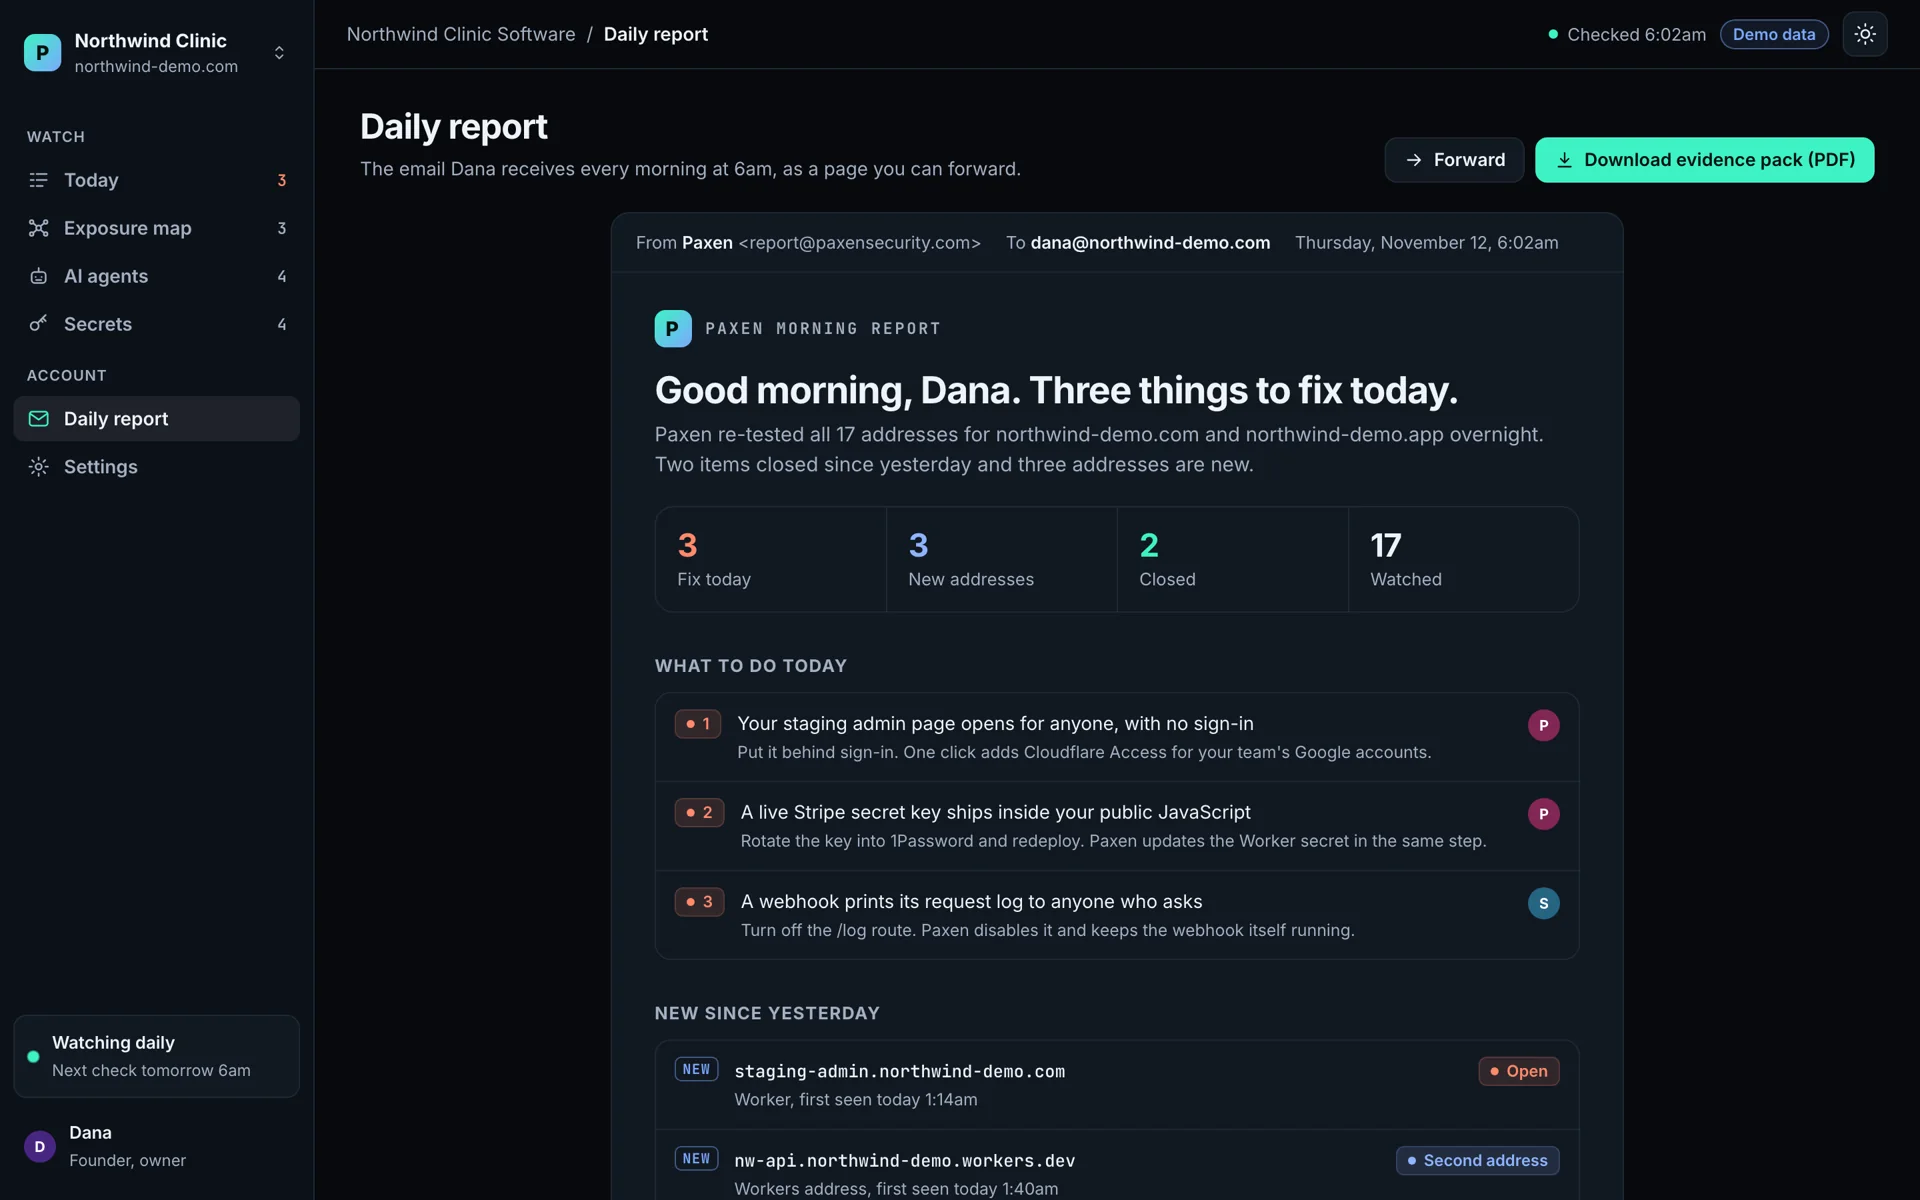
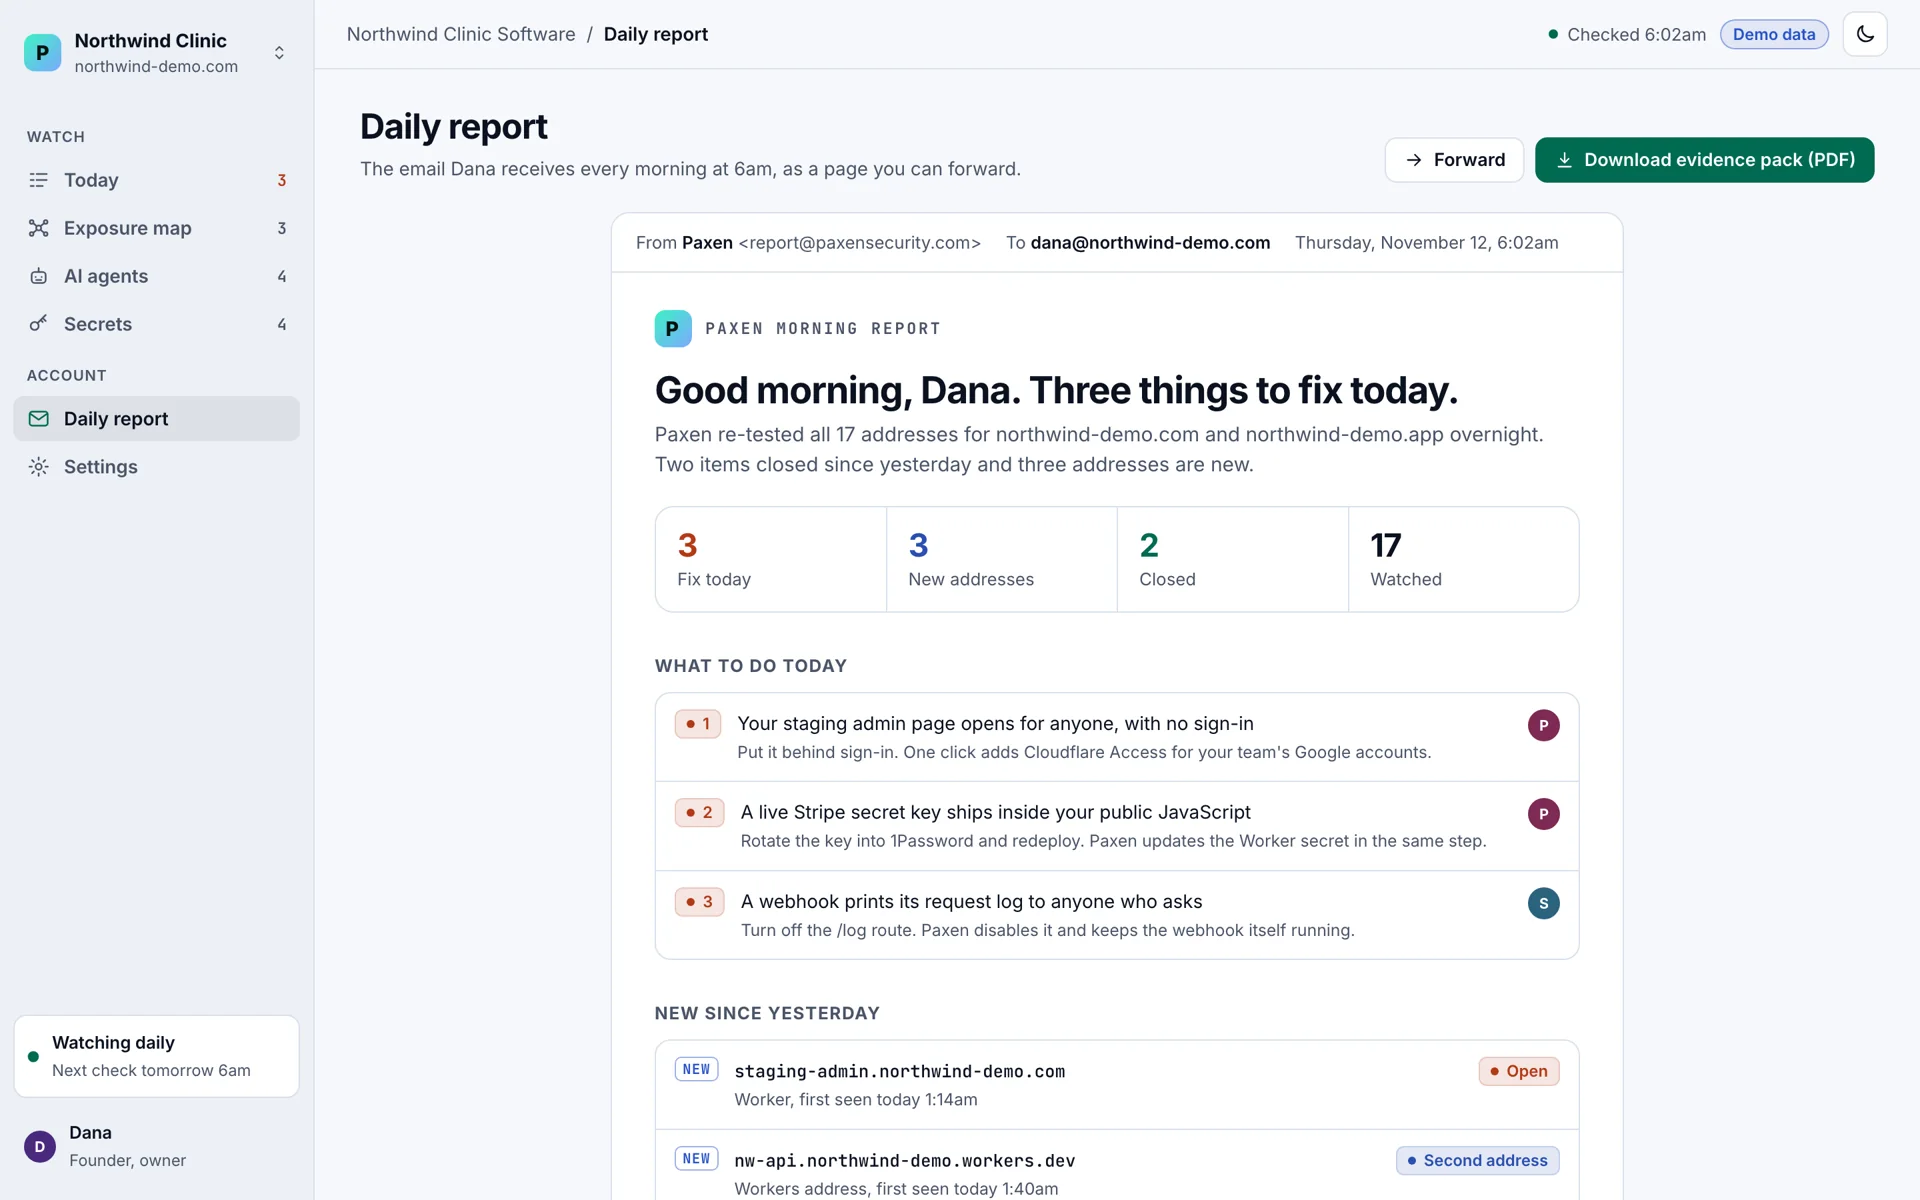
Your morning email shows what is newly exposed, what closed and the exact fixes for today. Paxen tracks your patch speed in days, from a published fix to yours, and once a week briefs you on attacker activity that applies to your stack. When a customer or insurer asks for proof, export the evidence pack built from your real state.
For your agents
Your own AI agents ask Paxen "what should I fix today?" and get the ranked list, each line with its one action and its owner.
# your agent asks
call paxen.fix_first({ "domain": "northwind-demo.com", "limit": 3 })

# Paxen answers
1  fix_today  settings route answers without sign-in  owner=priya
2  fix_today  live payment key in public script     owner=sam
3  this_week  workers.dev address beside booking       owner=priya
curl https://api.paxensecurity.com/v1/fix-first \
  -H "Authorization: Bearer $PAXEN_KEY" \
  -d domain=northwind-demo.com
When it matters
Today's footprint against yesterday's: a new open route or a forgotten workers.dev address is on your list before a stranger finds it.
Export an evidence pack with your pinned dependencies, patch speed, TLS and email setup, and every closed finding.
Hand your underwriter a current inventory of domains, keys, pins and agent permissions, built from your real state.
Contributor watch flags the new admin on your repository, and the agent inventory shows every token they can use.
Paxen names the key by pattern, checks whether it still works, and guides the rotation with the app updated in the same step.
Trust
The free scan reads public DNS and certificate records. Active checks run on domains you prove with a DNS TXT record, re-checked before every run.
_paxen.yourdomain.com TXTPaxen checks key values in place and reports each match by pattern name, so values stay out of every report and screen.
pattern: stripe_live_secretCloudflare, GitHub, Google and 1Password connect read-only, with every scope listed and one-click revoke. A one-click fix asks for the single permission it needs when you press it, and every action is logged.
scope: zone:read · workers:readProof
Epiphani Studios built Paxen with our own companies as customer zero, against two real bugs from our systems on November 12, 2026: a call-recording callback that sent a provider credential to any address a caller named, and a settings route that handed out a saved webhook address. Paxen catches both on the code as it stood before the fix and reports nothing on the fixed code.
POST /api/twilio/recording  RecordingUrl=paxensecurity.com/c/7f3a
canary hit  Authorization: Basic (length 92)
FOUND  a provider credential sent to a stranger's address

GET  /api/settings  200  "webhook": [Zapier hook address]
FOUND  a saved webhook address handed to anyone
POST /api/twilio/recording  RecordingUrl=paxensecurity.com/c/7f3a
403  provider signature required · no canary hit
clean

GET  /api/settings  401  sign-in required
clean
How Paxen compares
| Capability | Paxen | Aikido | Intruder | Coalition Control |
|---|---|---|---|---|
| Free first scan | Yes, no account | Yes | Yes | Yes, with an email |
| Ownership proof by DNS record before active tests | Yes | Yes | Account setup | Account setup |
| Plain-English list, one action and one owner per finding | Yes | Developer view | Ranked by exploit likelihood | Action plan and score |
| Inventory of AI agents with read, send, pay and delete | Yes | Not listed | Not listed | Not listed |
| Liveness check on every found key | Yes | Not listed | Not listed | Not listed |
| Pin actions, images and MCP servers by pull request | Yes | Not listed | Not listed | Not listed |
| API and MCP server for your own agents | Yes | Not listed | Not listed | Not listed |
Rival details read from each company's own pages on November 12, 2026 (linked above); "Not listed" means the capability was not on those pages.
Pricing
Your first scan takes about a minute and needs no account. Daily monitoring, the six modules and the connectors are paid plans.
Plan details arrive with your first daily report.
FAQ
Straight answers on safety, data and cost. Anything else: security@paxensecurity.com.
Yes. The free scan reads public certificate transparency records and DNS only, so your servers see no traffic from it. It takes about a minute and needs no account.
One DNS TXT record at _paxen.yourdomain.com proves you own the domain. It turns on the full active check set across your routes and pages, plus the daily rerun with a diff of anything newly exposed.
Exposure mapping, active checks and your morning email run every day. Campaign watch matches new supply-chain campaigns to your repos within the hour, and the AI code review runs every week.
The first scan is free and needs no account. Paid plans cover the daily rerun, the six modules and the connectors; join the list and the plan details arrive with your first daily report.
Connectors are read-only, with every scope listed and one-click revoke. Key values are checked where they live and never displayed, findings are kept so each morning can show what changed, and every action is logged.
Paxen works like an attacker across your whole footprint, every day, and writes for the owner: rules set severity, two model families cross-check the list, and every line carries one action and one named owner.
Yes. The Paxen API and MCP server let your agents ask "what should I fix today?" and pull the ranked list straight into their work.
Paxen comes from pax, Latin for peace: the peace of knowing your company is watched.
Map your public footprint in about a minute, free, with no account.
What answers on your domain right now? One minute, free.
Map it